What the Pentagon disclosed
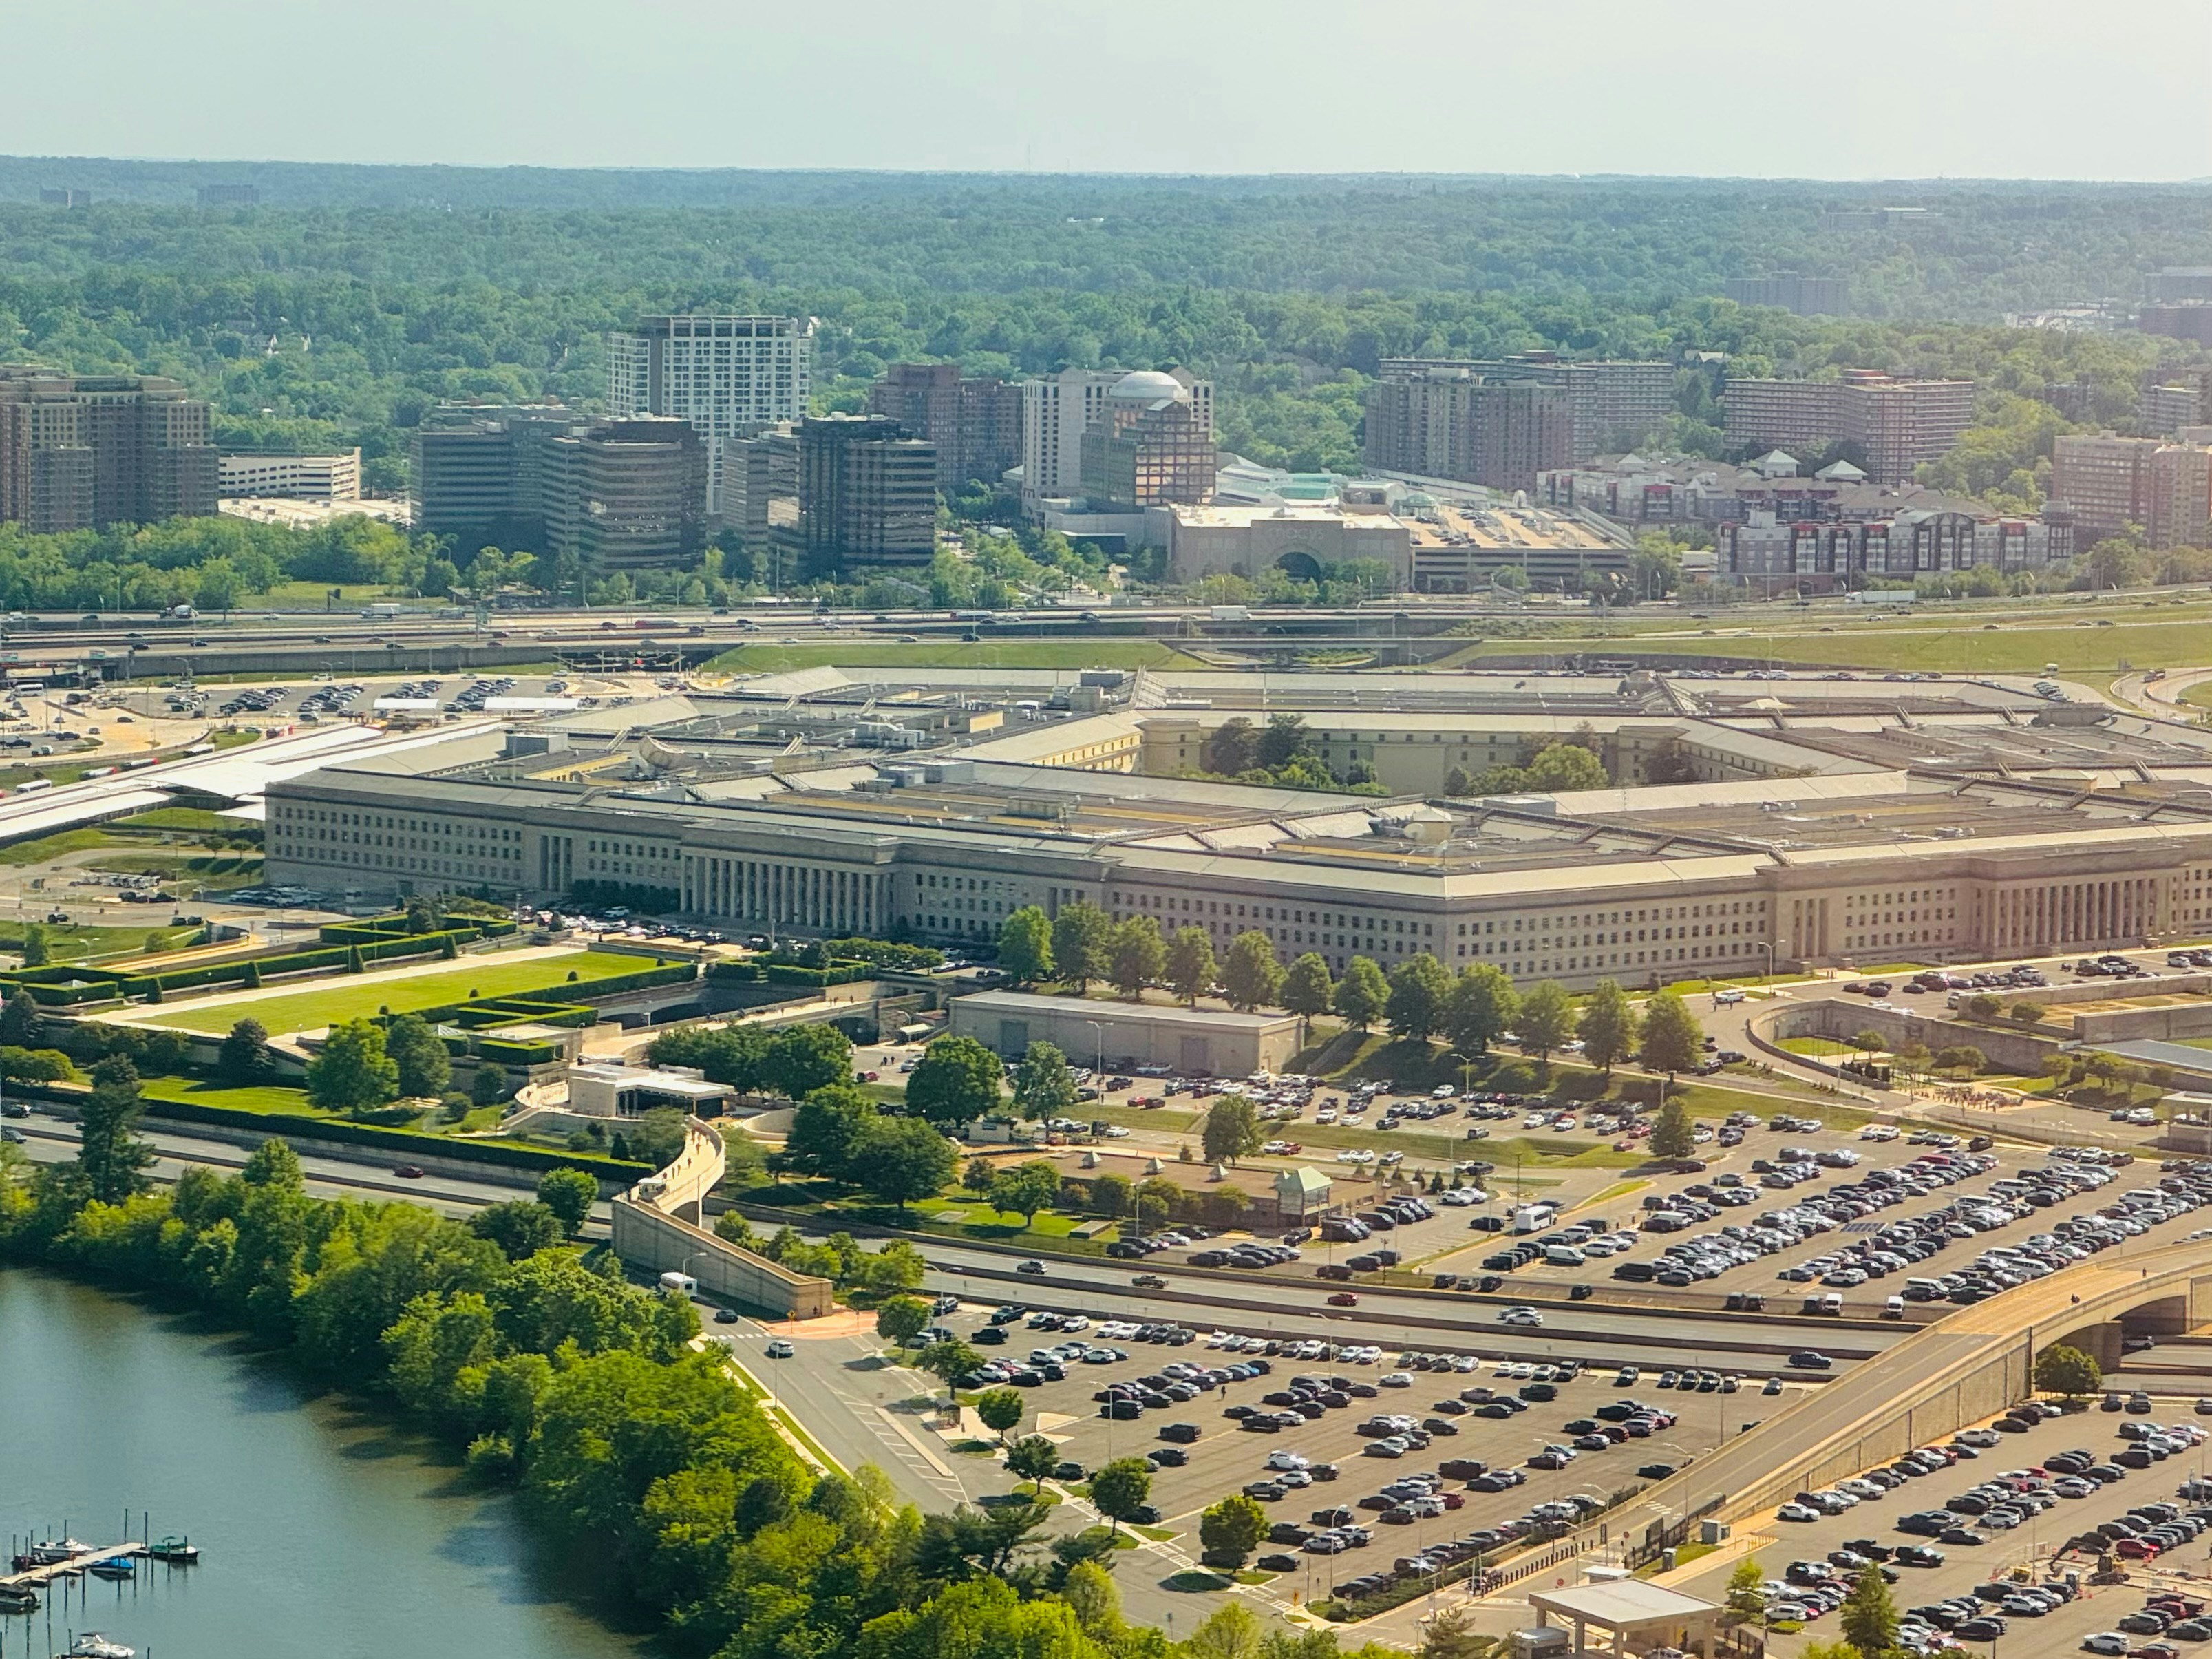
The Department of War sent breach notification letters informing affected people that the Defense Manpower Data Center, or DMDC, had been accessed by unauthorized users. The DMDC functions as a central personnel data system for the department, holding records on active-duty service members, civilian employees, veterans, retirees, and family members, more than 60 million people in total across its full history. The letter does not claim that every record in the system was accessed, and officials have not identified who the unauthorized users were, how they got in, or what their motive was, leaving affected individuals with a notification but very little actual context about the scope of their own exposure or the attacker behind it.
Independent reporting from CyberSecurityNews puts the number of people actually affected at approximately 2.76 million living individuals and around 294,000 deceased individuals, a combined figure north of 3 million. The access window ran from roughly October 2025 until the department discovered it on July 16, 2026, meaning unauthorized users had standing access to this data for about nine months before detection, not nine days or nine weeks.
The detail that should alarm every CTO
The data exposed includes Social Security numbers, full names, dates of birth, contact information, sex, race, and military-specific personnel information such as occupational specialty. None of it was encrypted, according to the disclosure. The breach notification does not explain why a system holding this category of data for this many people was storing it in plaintext, and officials have offered no public justification beyond confirming the fact itself, which leaves the most important question in the entire disclosure unanswered.
This is not a system CTOs can dismiss as someone else's problem because it belongs to a defense agency. The DMDC is, by any reasonable standard, a mature, well-resourced, heavily regulated environment, exactly the profile that security leaders often point to as the bar their own organization is trying to clear. If a system with that profile was storing unencrypted Social Security numbers for nine months without detection, the assumption that organizational maturity guarantees encryption at rest does not hold, and should not be relied on as a substitute for actually checking.
Why nine months of undetected access matters more than the record count
A breach discovered within hours or days limits the damage even when the underlying data is sensitive, because the exposure window is short and the response can be fast. A nine-month dwell time means the unauthorized access generated no alert, triggered no anomaly detection, and was caught only through whatever process finally surfaced it on July 16. That gap between compromise and detection is often the more expensive failure than the initial access point itself.
For a dataset of this sensitivity, that length of undetected access suggests the monitoring layer sitting on top of the data, not just the encryption underneath it, was not calibrated to notice unusual access patterns against a system holding Social Security numbers for millions of people. Encryption at rest and access anomaly detection are two separate controls, and this incident suggests both were either absent or ineffective for the better part of a year.
The remediation gap: credit monitoring versus permanent exposure
The Pentagon's offered remedy, one year of free credit monitoring through IDX, is the standard industry response to this class of breach, and it is also clearly mismatched to the actual risk. A Social Security number cannot be reissued the way a credit card number can, and a monitoring service that expires in twelve months does nothing about the risk of misuse in year two, five, or ten. The letter itself acknowledges this tension by noting SSNs are very difficult to change, meaning the consequences for affected individuals could last a lifetime even though the offered protection does not.
Officials say there is no evidence the data has been misused yet, which is a reasonable thing to say and also not a reassurance that holds up over the long timeframe this type of exposure actually carries. CTOs evaluating their own breach response plans should treat 'no evidence of misuse yet' as a snapshot, not a conclusion, and build remediation offers around the actual lifespan of the risk rather than a standard twelve-month vendor contract. Fraud involving stolen Social Security numbers frequently surfaces years after the original exposure, once the data has circulated through enough criminal marketplaces to reach someone willing to use it, which is precisely the period a single year of monitoring will have already lapsed.
The audit every CTO should run this month
The direct, actionable response to this disclosure is an internal audit of which production and archival databases actually encrypt sensitive fields at rest, confirmed by checking the storage layer directly rather than trusting a policy document that says encryption is required. Policy documents and actual configuration drift apart constantly, especially in systems that have been in production for years and passed through multiple teams, migrations, and vendors without anyone re-verifying the original security assumptions.
Pair that encryption audit with a review of access anomaly detection on any data store holding regulated personal information: Social Security numbers, financial account data, or health information. If a breach of similar scale sat undetected in your environment for nine months, would current logging and alerting actually catch it, or would detection depend on the same kind of fortunate discovery that eventually surfaced this one at the Pentagon? Most organizations have not tested that question honestly, largely because doing so requires admitting that the answer might be no, and budgeting accordingly rather than renewing the same monitoring contract on autopilot for another year.