From a hotel in Osaka to a German cell
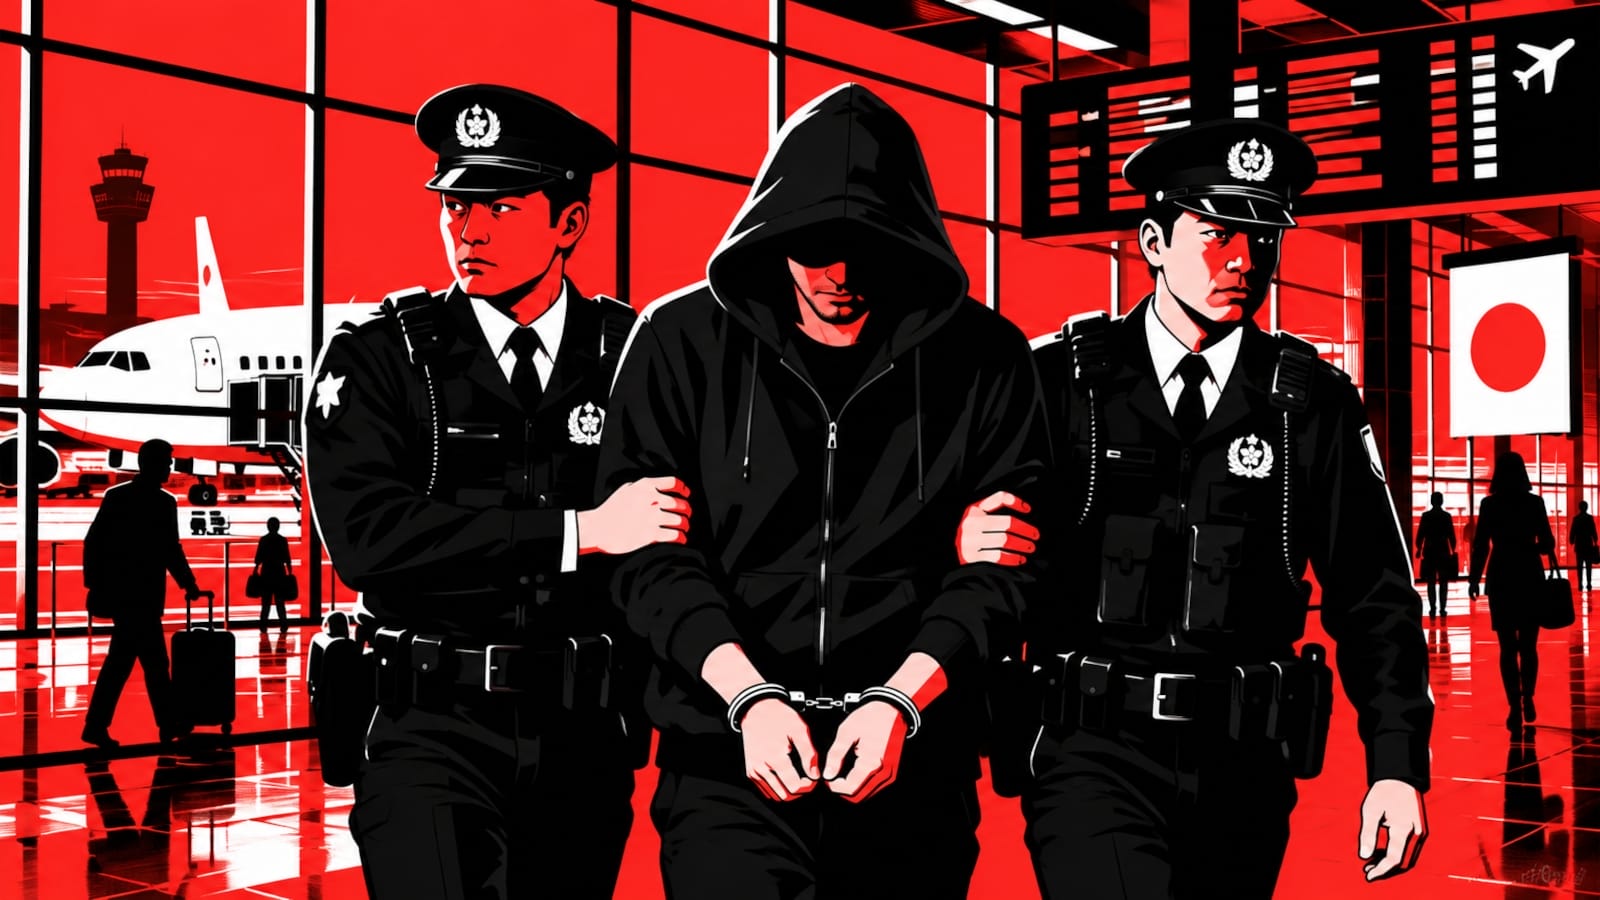
Japan's National Police Agency confirmed on October 8 that a Russian national suspected of being a leading member of the Qilin ransomware group has been extradited to Germany, where authorities had obtained an arrest warrant tied to a ransomware incident there. The man was first detained by Japanese police after arriving in the country as a tourist, with media reporting in May that he had been held at a hotel in Osaka under Japan's Extradition Law before the transfer. Japanese outlets reported the October handover on October 6, and the NPA's confirmation followed two days later.
The case was a joint effort between Japan's Ministry of Justice, the Tokyo High Public Prosecutors Office, and German authorities, underscoring how far law enforcement is now willing to reach across jurisdictions to get a ransomware suspect in front of the right court. The article does not name the man or detail the specific German incident behind the warrant, but the extradition itself, from an unrelated third country where he was traveling, is the significant part. It means operators can no longer assume that staying off the territory of a victim nation is sufficient protection.
What Qilin actually did to earn this much attention
Qilin is not a marginal player. The group emerged in August 2022 under the name Agenda and has since been tied to more than 2,350 known organizations across 62 countries, running a double extortion model that steals data before encrypting it so victims face both a ransom demand and a leak threat. Since June alone, it has listed more than 450 victims on its leak site, a pace that puts it among the most active ransomware-as-a-service operations currently running.
The named victim list reads like a cross-section of global enterprise: Nissan, Asahi, Lee Enterprises, Court Services Victoria, and the U.S. Bureau of Alcohol, Tobacco, Firearms and Explosives all appear as confirmed targets. The Asahi attack alone disrupted operations for an extended period and exposed data belonging to roughly 1.5 million people, which gives a sense of the operational and reputational scale a single successful Qilin intrusion can reach when it lands on the wrong target.
The initial access story matters as much as the encryption
Qilin's affiliates have been linked to exploitation of Check Point VPN zero-days and Palo Alto VPN n-day vulnerabilities to gain initial access, which puts this group squarely in the category of ransomware operations that treat perimeter VPN appliances as a primary way in rather than a hardened edge. That pattern tracks with what the broader ransomware landscape has looked like all year: edge devices meant to secure remote access have repeatedly become the entry point attackers use to get past that same security.
For any organization running Check Point or Palo Alto VPN infrastructure, this is a direct reminder that patch cadence on edge appliances is the first line of defense against exactly the kind of operation that just had a leader extradited. The zero-day and n-day distinction matters here too: n-day exploitation means Qilin affiliates were successfully hitting targets that had not yet applied already-available patches, which is the most preventable category of compromise in the entire ransomware kill chain.
Arrests are getting faster and more international
This extradition does not happen in isolation. It follows a stretch of high-profile law enforcement action against ransomware and extortion actors generally, including arrests tied to the ShinyHunters extortion group within the same week, and it reflects a broader shift where international cooperation on ransomware cases has visibly accelerated over the past year. Operators who once assumed years of relative safety behind jurisdictional gaps are now watching peers get picked up on tourist visas in third countries and handed over within months.
That shift has real strategic value for defenders, even if it does not show up in a vulnerability scan. Deterrence against ransomware operators has always been weak relative to the financial incentive, and arrests like this one are one of the only forces that move that calculation at all. It will not stop Qilin's affiliate network from running attacks this week, since ransomware-as-a-service operations are built to survive the loss of any single person, but it changes the long-run risk calculus for anyone weighing whether to stay in this business.
What this changes, and what it does not, for your risk model
Do not update your threat model to assume Qilin is weakened. RaaS operations are deliberately structured so that leadership arrests disrupt but rarely dissolve them, and a replacement leader, a rebrand, or an affiliate migration to another active group are all more likely near-term outcomes than the brand disappearing. The practical defensive posture against Qilin, and against ransomware generally, does not change because of one arrest: patch VPN appliances fast, segment so a single compromised credential cannot reach everything, and maintain offline backups that double extortion cannot also encrypt.
What should change is how you weigh ransom negotiation and law enforcement engagement if you are ever on the receiving end of an attack from a named, actively prosecuted group like this one. Every arrest and extradition adds to a body of evidence and intelligence that law enforcement can bring to bear faster than it could even a year ago, which is one more reason to involve the FBI or equivalent agency early in any live incident rather than treating the ransom negotiation as a purely private transaction.