A modem bug that needed nothing from the victim
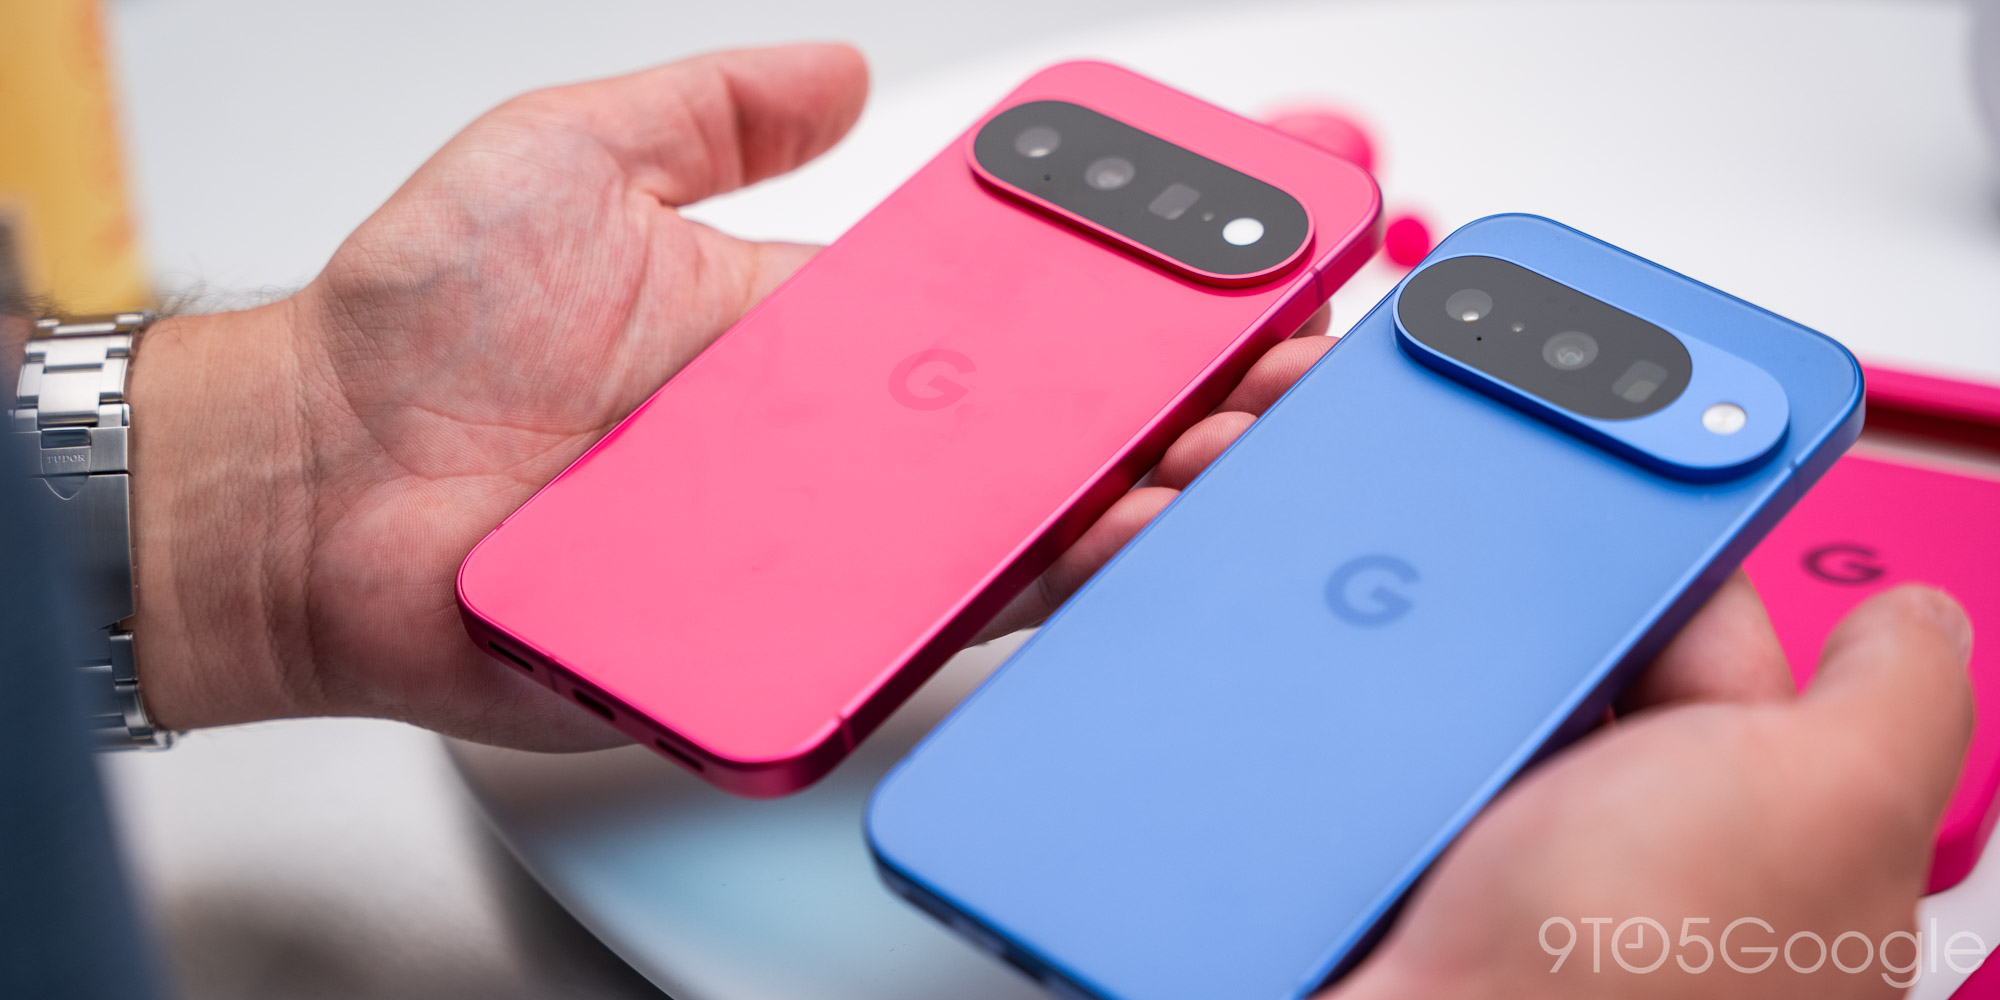
Google disclosed CVE-2026-58704 on September 16 as part of its monthly Pixel security bulletin, describing a permission bypass in the device's cellular modem caused by a logic error in how the baseband handles certain requests. The flaw allowed what Google's own advisory called remote, proximal, or adjacent escalation of privilege with no additional execution privileges needed, and critically, no interaction from the phone's owner at any point in the attack chain.
That zero-click quality is what separates this bug from the vast majority of mobile vulnerabilities enterprises train users to defend against. Phishing awareness, careful link clicking, and app vetting policies exist to interrupt attacks that need a victim to do something. A zero-click modem exploit needs nothing from the target beyond having a phone powered on and connected to a cellular network, which describes essentially every device an organization issues to staff.
Confirmed targeting, undisclosed targets
Google confirmed the flaw was exploited against a limited number of Pixel devices before the patch shipped, language that in mobile security disclosures typically signals a commercial spyware operation or a nation-state actor rather than opportunistic cybercrime. The company declined to comment further on who was affected or who built the exploit when reporters asked directly, a common posture for vendors managing active investigations alongside law enforcement or affected customers.
The lack of detail leaves enterprise security teams without the specifics they would need to assess whether their own executive or field device fleet fell inside the actual blast radius. What is known is that the targeting was narrow rather than mass-market, consistent with the pattern seen in prior baseband and modem-level exploits that tend to concentrate on journalists, executives, diplomats, and other individuals worth the cost of a bespoke exploit chain.
Baseband attacks sit below most enterprise security controls
The cellular modem, or baseband processor, runs its own firmware separate from the phone's main operating system and typically has direct access to memory and hardware that the OS-level security sandbox was never designed to police. Mobile device management platforms, endpoint detection agents, and app-layer controls that enterprises rely on for phone security largely have no visibility into baseband behavior at all, since those tools were built to monitor the application layer where user-installed software runs, not the firmware layer beneath it.
That blind spot makes baseband bugs disproportionately valuable to sophisticated attackers precisely because the defensive tooling enterprises have already bought and deployed cannot see the attack happening. A compromised modem can potentially access call data, location, and network traffic before any OS-level security control gets a chance to inspect or block it, which is why baseband exploits routinely command a premium price on the exploit broker market compared to app-layer bugs. Vendors selling access to these chains typically price them well into six or seven figures, a range that only nation-state budgets and the most well-funded commercial spyware operations can realistically sustain.
CISA's catalog addition puts this on the federal patch clock
CISA added CVE-2026-58704 to its Known Exploited Vulnerabilities catalog following Google's disclosure, formally confirming the exploitation and setting a remediation deadline for federal agencies running Pixel fleets. For government and defense-adjacent contractors that issue Pixel hardware specifically because of its faster security update cadence compared to other Android OEMs, this incident is a reminder that faster updates reduce the exposure window and still leave a gap that a well-resourced attacker with a zero-day can exploit before any patch exists.
The broader September 2026 Pixel security bulletin patched more than 200 vulnerabilities total, a volume that reflects both the complexity of modern smartphone software stacks and the intensity of research attention Pixel devices receive as Google's flagship reference platform for Android security work. Enterprises should treat the full bulletin as mandatory reading, not just the one CVE that made headlines, since several of the other 200-plus fixes address issues with similar remote-exploitation potential that simply have not been weaponized yet.
Executive device fleets need a different threat model
Most enterprise mobile security programs are built around a threat model calibrated for commodity malware and phishing, which is the right calibration for the average employee's device but badly undersized for anyone whose phone is a plausible espionage or extortion target. General counsel, finance executives, and anyone traveling to jurisdictions with active state surveillance programs fall into a different risk category entirely, one that most mobile policies never explicitly name or budget for separately.
That smaller population deserves its own control set: faster mandatory patch enforcement measured in days rather than the standard 30-day window, consideration of hardened device modes like Apple's Lockdown Mode or Android's equivalent restrictions, and periodic forensic checks from a mobile threat defense vendor capable of detecting baseband-level compromise indicators that standard MDM tooling simply cannot see. Building this tier does not require replacing the fleet, it requires writing a shorter patch SLA and assigning real budget to the handful of devices that actually need it.
What this means for the roadmap
This incident should push security leaders to separate mobile device risk into tiers rather than applying one policy to every phone in the fleet. A finance clerk's phone and a CFO's phone carry meaningfully different threat profiles, and treating them identically wastes protection budget on the low-risk population while leaving the high-risk one under-defended against exactly the kind of targeted, zero-click attack Google just patched for Pixel owners this month.
Budget planning for next year should include a line item for mobile threat defense tooling with baseband and network-layer visibility for the executive and field-staff tier specifically, alongside a hard patch SLA that does not wait for the standard monthly cycle when a CISA KEV entry is involved. The alternative is discovering a compromise only after the exfiltrated data surfaces somewhere else, when the incident response bill is already far larger than the tooling would have cost.