The billing portal was the weak point, not the product
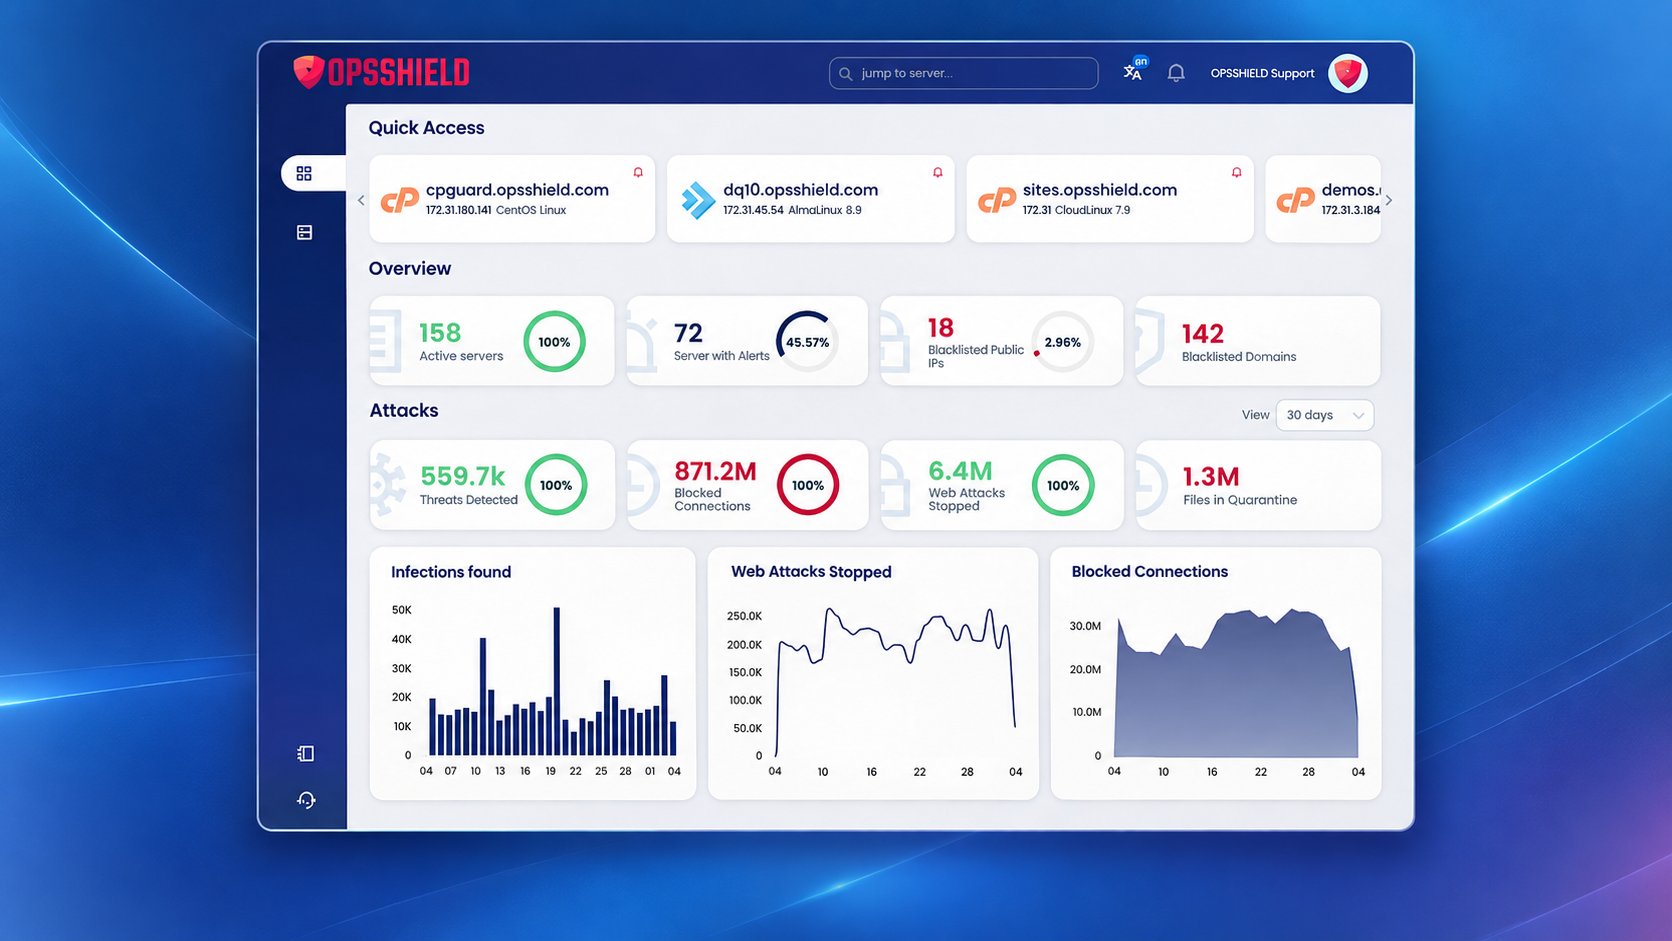
cPGuard is a privileged Linux security agent built by OPSSHIELD and widely deployed across web hosting environments, where it runs with elevated access to monitor and protect customer servers. The attack that compromised it left the actual codebase untouched throughout. On November 1, an attacker registered an ordinary trial account and spent time studying how the product's licensing system communicated with its backend, then used crafted requests against OPSSHIELD's billing portal to achieve unauthorized command execution on the billing and licensing server itself. That server sits adjacent to the product but handles an entirely different function: tracking customer accounts, subscriptions, and payment status rather than shipping the agent's own code.
That initial foothold, reached through a customer-facing business system rather than the security product's engineering pipeline, is what gave the attacker an update-storage key. With that key in hand, they could push whatever they wanted through cPGuard's trusted, automatic update mechanism, which is precisely the capability that makes a security agent dangerous once it is turned against the customers who trust it. The irony is pointed: the very automation that makes privileged security agents useful at scale, pushing protective updates to thousands of servers without manual intervention, is what let one compromised billing credential become a root-level compromise of nearly 3,000 machines in under eighty minutes.
Nearly 3,000 servers, root access, in under 80 minutes
Between 02:08 and 03:20 UTC on November 2, the attacker distributed malicious cPGuard versions 5.88.12 through 5.88.19 through the compromised update channel. Approximately 2,950 Linux servers pulled and installed one of those poisoned versions in that window, and because cPGuard runs with root privileges by design, the malicious code executed with full administrative control on every affected machine. The speed of the rollout matters as much as the scale: a window of just over an hour was enough to reach nearly three thousand independent server environments, each presumably belonging to a different hosting customer with its own downstream users and data.
Andrew Obadiaru, vice president and CISO at Cobalt, framed the structural problem cleanly: a privileged security agent with automatic updates can turn a single compromised credential into access across an entire customer base. That is the trade-off every organization running a privileged, auto-updating agent has implicitly accepted, usually without examining it closely, because the alternative of manually reviewing and approving every security update is its own operational burden most teams are not staffed to carry. This incident is the concrete cost of that trade-off made visible, and it should prompt a harder look at how much unilateral push authority any single vendor credential is allowed to hold.
What the malicious update actually stole
The payload was comprehensive. It harvested Linux password hashes, root SSH keys, database credentials where present, shell history that may contain additional secrets typed into terminal sessions, and cloud storage credentials on some servers. It installed a hidden root shell at a disguised filesystem path and uploaded collected data back to OPSSHIELD's own licensing infrastructure for later retrieval, meaning the attacker effectively used the vendor's legitimate infrastructure as a drop point for stolen material from the vendor's own customers. Every one of those credential types is reusable well beyond the compromised server itself: a stolen database credential or cloud storage key is a direct path into systems that never ran cPGuard at all.
OPSSHIELD's initial advisory estimated attackers retrieved 32 collected files, each tied to a different customer server, though the company has been clear that figure is preliminary and does not establish the full extent of what was taken. Separately, the breach exposed roughly 7,900 billing-account records containing personal information and bcrypt-hashed passwords, confirming that customer business data, alongside server-level credentials, was also caught up in the compromise. Any customer running an affected version should assume credential exposure until their own investigation proves otherwise, rather than waiting for OPSSHIELD's scope assessment to narrow further.
The response, and what it leaves unresolved
OPSSHIELD has released corrective versions 5.88.25 and 5.88.26 along with additional cleanup measures, revoked the compromised update-storage credentials, and begun rebuilding affected infrastructure. Its guidance to customers is blunt: where interactive attacker access on a server can be confirmed, rebuild from a clean backup that predates November 1 rather than attempting to clean the compromised system in place. For systems where integrity cannot be established either way, it recommends rebuilding anyway rather than assuming they escaped the campaign.
What remains open is the full scope of follow-on damage. Investigators are still working through how much of the harvested credential data has been or will be used for further intrusions into the nearly 3,000 affected environments, each of which may have its own downstream customers, databases, and cloud accounts now reachable through stolen keys. That tail risk, not the initial 80-minute compromise window, is what security teams running any OPSSHIELD product should be tracking closely in the weeks ahead.
The lesson for every vendor with privileged auto-update access
This incident is a clean illustration of why supply chain risk assessments that focus only on a vendor's product security posture miss half the picture. The vulnerability that mattered here lived in a billing portal, a system most customers never think about and most vendor security reviews treat as lower priority than the core product. Any system that can reach an update-signing or update-storage key, however indirectly, deserves the same scrutiny as the product it feeds.
For CTOs evaluating or already running privileged security agents, the practical takeaway is to ask vendors directly how their business systems are segmented from their update infrastructure, and whether a compromise of billing, licensing, or customer support tooling could realistically reach the mechanism that pushes code to your servers. If a vendor cannot answer that clearly, assume the answer is no, and weight that into how much blast radius you are willing to accept from a single agent running with root across your fleet.