What happened inside Cursor's marketplace
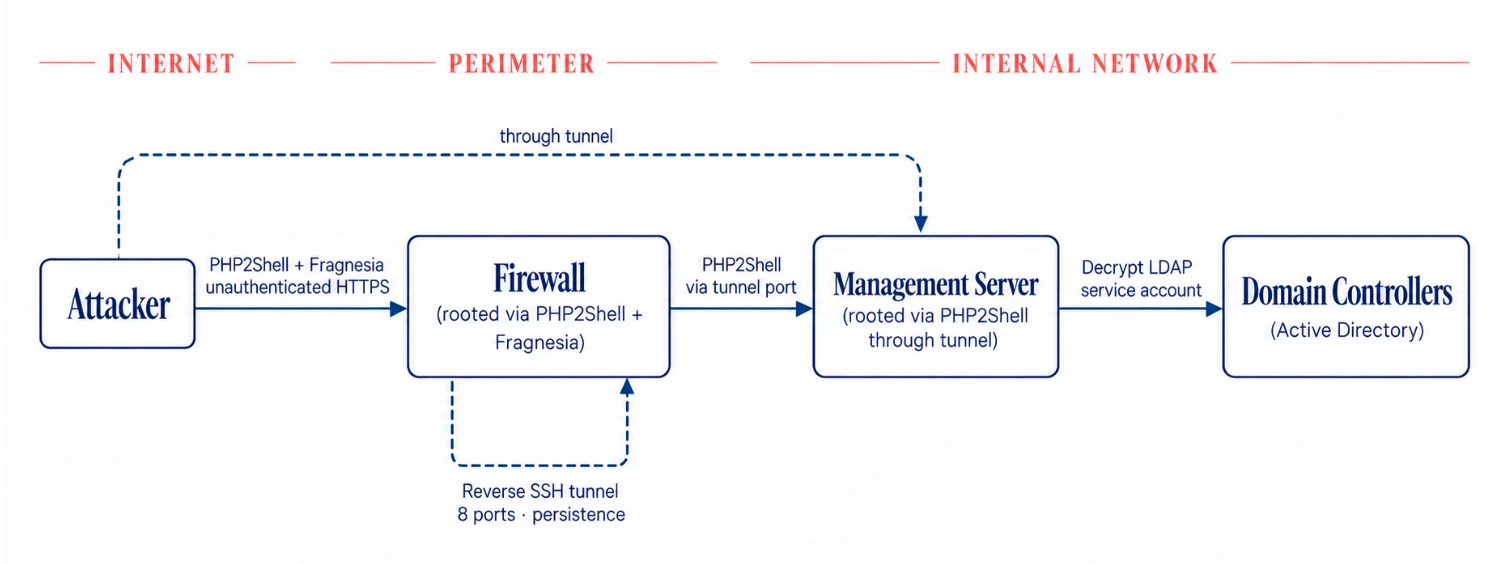
A tampered version of Anthropic's Claude Code extension made it into Cursor's VS Code extension marketplace and stayed available for approximately 11 hours before Cursor identified and removed it. Developers who installed the compromised build on October 29 got more than a coding assistant: the extension collected information about the host machine and attempted to install a persistent backdoor over SSH, built to survive even if the user later removed the extension itself, which means a simple uninstall would not have been enough to clear an infected machine.
The backdoor's design included scripts that tried to reconnect to the attackers' command-and-control server every minute, which is the kind of persistence mechanism normally associated with dedicated malware rather than a tampered developer tool. Cursor says it has since found no evidence that any other extension in its marketplace was similarly compromised, and that it worked with the hosting provider of the attacker's server to take it offline, cutting the live command channel even for machines that had already been infected during that 11-hour window.
Why the backdoor mostly didn't work, and why that's not reassuring
Cursor's own assessment is that flaws in the backdoor's code made it unlikely to function correctly in many cases. That's a genuinely lucky break, but it's luck, not design. The attacker got a tampered extension into a legitimate marketplace, had it run with the user's local permissions, and executed a credential and persistence attack chain against developer machines, the exact machines that typically hold SSH keys, cloud credentials, and source code access. The only thing that limited the damage was a bug in the attacker's own tooling.
Cursor's public response included removing the extension, taking down the attacker's infrastructure with the hosting provider's help, and temporarily shutting down and rebuilding its entire marketplace rather than patching around the specific incident. That's a reasonable level of caution, but it also signals Cursor itself wasn't confident it could rule out broader compromise quickly, which matters for any enterprise that has Cursor extension installs running at scale across its developer fleet.
Who's affected and what Anthropic said
Reporting on the incident puts the number of affected users at roughly 5,000, drawn from Cursor's own disclosure. Anthropic, whose brand and product name were directly impersonated in the tampered extension, stated that the incident only impacts Cursor users and was unrelated to its own systems or infrastructure. That's an important distinction for any organization running Claude Code through Anthropic's own channels rather than through Cursor's marketplace distribution, since the compromise lived entirely in the distribution layer rather than in Anthropic's model or API.
Affected users who installed the compromised build on October 29 are being urged to check their machines for signs of infection, remove any unauthorized SSH access that may have been established, and rotate credentials that could plausibly have been exposed. For a developer machine, that list of credentials is rarely short: cloud provider keys, git hosting tokens, internal service credentials, and whatever else accumulates in a typical engineer's environment over time, often undocumented anywhere a security team would think to check during a routine audit.
What security researchers are actually worried about
Eerke Boiten of De Montfort University put the concern in blunt terms, saying the prospect of coding assistants sending out poisoned agents at scale is more worrying than the risks the security community was already tracking before AI tooling became standard in developer workflows. Alan Woodward of the University of Surrey framed it as a case where the industry's attention has been fixed on large language models attacking other systems, while this incident ran the more familiar playbook of attacking the LLM-powered tool itself through its distribution channel, the part of the supply chain security teams audit least often.
ESET's Jake Moore made the point that matters most for enterprise risk calculus: 5,000 affected users sounds small in absolute terms, but these are developers, a population with outsized access to source code, infrastructure, and credentials relative to almost any other employee category in the business. A compromised sales rep's laptop is bad. A compromised engineer's laptop, with live SSH keys and repo access, is a different category of exposure entirely, and the math on blast radius per compromised machine simply does not compare.
What this means for your developer tooling policy
If your engineering org uses Cursor, or any AI coding assistant distributed through a third-party extension marketplace, this is the moment to ask a specific question: do you actually know which extensions, and which versions, are installed across your developer fleet right now, or would you be reconstructing that list reactively during an incident. Most engineering organizations cannot answer that question today, and this incident is exactly the scenario where that gap turns into lost time during response.
More broadly, this is the second incident this quarter involving a compromised AI coding tool distribution channel, following the AGENTS.md hijack risk disclosed in prior coverage. The pattern is consistent enough now to warrant a policy response rather than a one-off response: treat AI coding assistant extensions with the same supply-chain scrutiny you'd apply to any dependency with broad local execution rights, including pinned versions, marketplace allowlists, and monitoring for unexpected outbound connections from developer endpoints. None of that requires exotic tooling, it requires treating the extension marketplace as production infrastructure rather than a convenience developers manage for themselves.