What actually changed on August 2
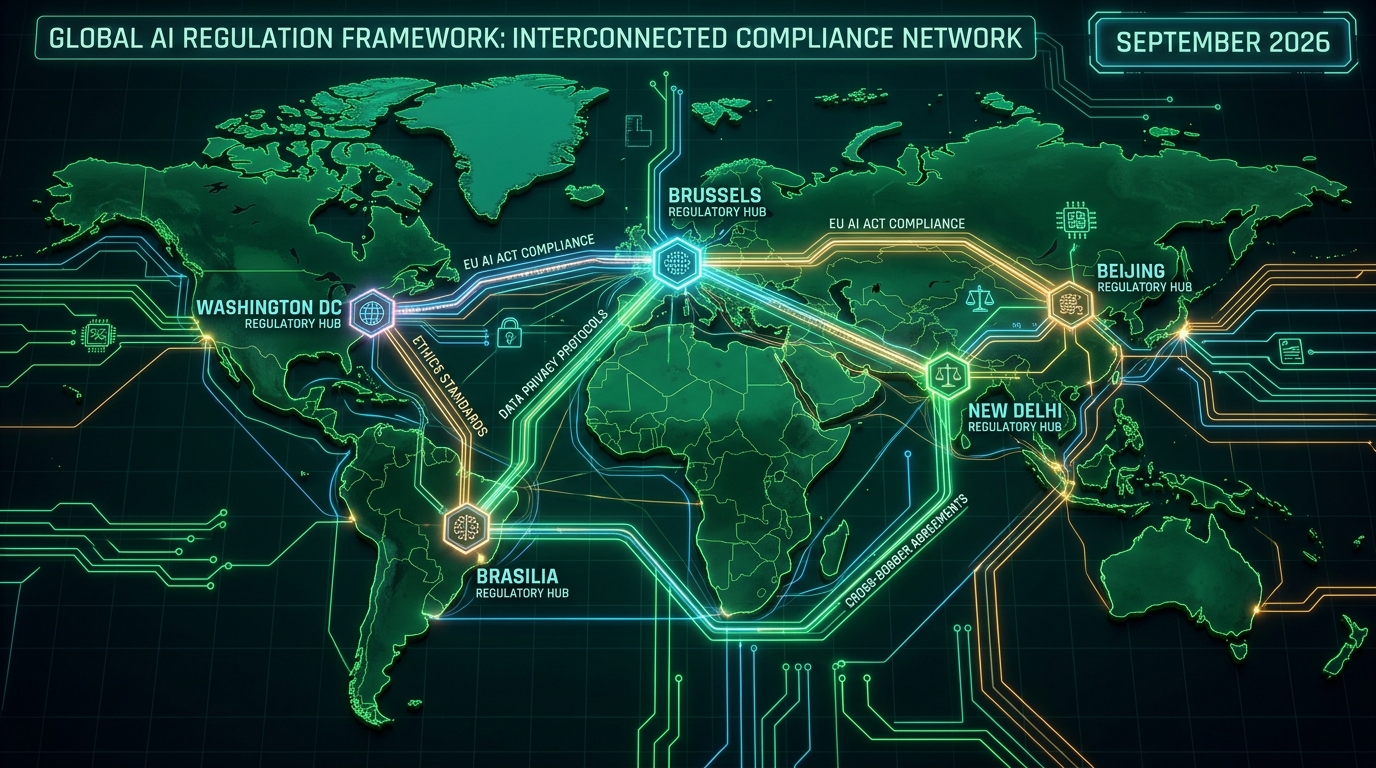
The European Commission's AI Office began enforcing two distinct sets of obligations as of August 2, 2026. Article 50 transparency requirements now apply to systems interacting directly with people: chatbots, AI agents, avatars and similar interfaces must disclose that users are interacting with an AI system unless that fact is already obvious from context, and that disclosure must appear from the start of the first interaction, clear, distinguishable and accessible rather than buried in terms of service.
Separately, general-purpose AI model providers now face binding obligations to maintain technical documentation, notify downstream providers of relevant model information, adopt a policy demonstrating compliance with EU copyright law, and publish a summary of training content. Non-EU providers must appoint an authorized representative within the EU, and models identified as carrying systemic risk face additional evaluation, risk-management and cybersecurity duties layered on top of the baseline requirements.
The synthetic content marking rules enterprises will feel first
Providers must now mark AI-generated or manipulated synthetic audio, images, video and text with machine-readable indicators, a requirement that touches marketing, content production and customer communication workflows across nearly every enterprise using generative AI tools in any customer-facing capacity. Deployers face a parallel obligation to disclose deepfakes and AI-generated text specifically on matters of public interest, with an exception carved out for content that has undergone editorial human review.
For enterprises running AI-assisted content pipelines that touch European markets, this is the requirement most likely to require actual engineering work rather than pure documentation: verifying that content marking metadata survives every step of a publishing pipeline, across formats, platforms and languages, is a nontrivial technical task, and 'we didn't realize the marking got stripped during transcoding' is not a defense regulators are likely to find persuasive.
The penalties are calibrated to worldwide revenue, not EU revenue
Violations of transparency requirements and general-purpose AI obligations carry fines up to 15 million euros or 3 percent of worldwide annual turnover, whichever is greater, while violations involving prohibited AI practices carry a steeper ceiling of up to 35 million euros or 7 percent of worldwide turnover. Calculating penalties against worldwide turnover rather than EU-specific revenue means the Act's financial exposure for a large multinational dwarfs what a purely EU-revenue-based calculation would produce, a structure mirroring GDPR's own penalty design.
Enforcement authorities are directed to weigh gravity, duration and intent when setting penalties within those ranges, which gives companies a real incentive to demonstrate good-faith compliance efforts even where full technical compliance is still in progress. A documented, active remediation plan is likely to matter meaningfully in how aggressively a violation gets penalized compared to a company that made no visible effort to comply before enforcement began.
High-risk systems get more runway, but the classification work starts now
The Act's core high-risk system requirements, the category covering AI used in employment decisions, credit scoring, critical infrastructure and similar consequential domains, are postponed to December 2, 2027 for stand-alone systems and August 2, 2028 for systems embedded in regulated products. That postponement gives companies real additional time before the most operationally demanding obligations bite.
But the postponement is not a reason to wait before starting classification work. Companies should be mapping which of their systems fall under Annex III's high-risk specifications now, while the compliance deadline is still comfortably in the future, rather than treating 2027 as a problem for a later budget cycle. Classification is foundational to every other compliance decision that follows, and doing it under time pressure closer to the deadline is a materially worse position than doing it deliberately now.
Why 'we have no EU office' does not exempt anyone
The Act's territorial reach is broader than many US companies initially assume. It applies to any company that places an AI system or model on the EU market, puts an AI system into service in the EU, supplies AI output that gets used in an EU business process, or otherwise operates in a covered role, provider, deployer, importer, distributor or manufacturer, serving the EU market, regardless of whether that company has any physical or legal establishment in Europe.
That last category, supplying AI output used in an EU business process, is the one most likely to catch companies by surprise. A US software vendor with no EU office, no EU sales team and no stated intention to operate in Europe can still fall under the Act's scope if an EU customer's business process incorporates that vendor's AI-generated output, which is a far lower bar for applicability than most US legal and compliance teams initially assume when scoping their EU AI Act exposure.
The six-step action list for compliance teams
Legal guidance around the enforcement date converges on a consistent sequence: map every EU connection, including customers, distributors and business processes touched by AI output; assign the correct legal role for each system under the Act's framework; classify every system by its prohibited, transparency, general-purpose, systemic or high-risk status; test that disclosures and content markings actually function correctly across products, devices and languages; collect and preserve compliance evidence including technical documentation and testing records; and update internal governance to allocate documentation, cooperation, audit and incident-response responsibilities clearly across the supply chain.
For CIOs and general counsel working through this list jointly, the practical starting point is the mapping step, since it determines the scope of everything that follows and is likely to surface AI touchpoints with EU business processes that other parts of the organization were not tracking as a compliance concern. Treating that mapping exercise as a one-time project rather than an ongoing inventory process is the most common mistake companies make as they build out their EU AI Act compliance program.