A security chief who has done this three times before
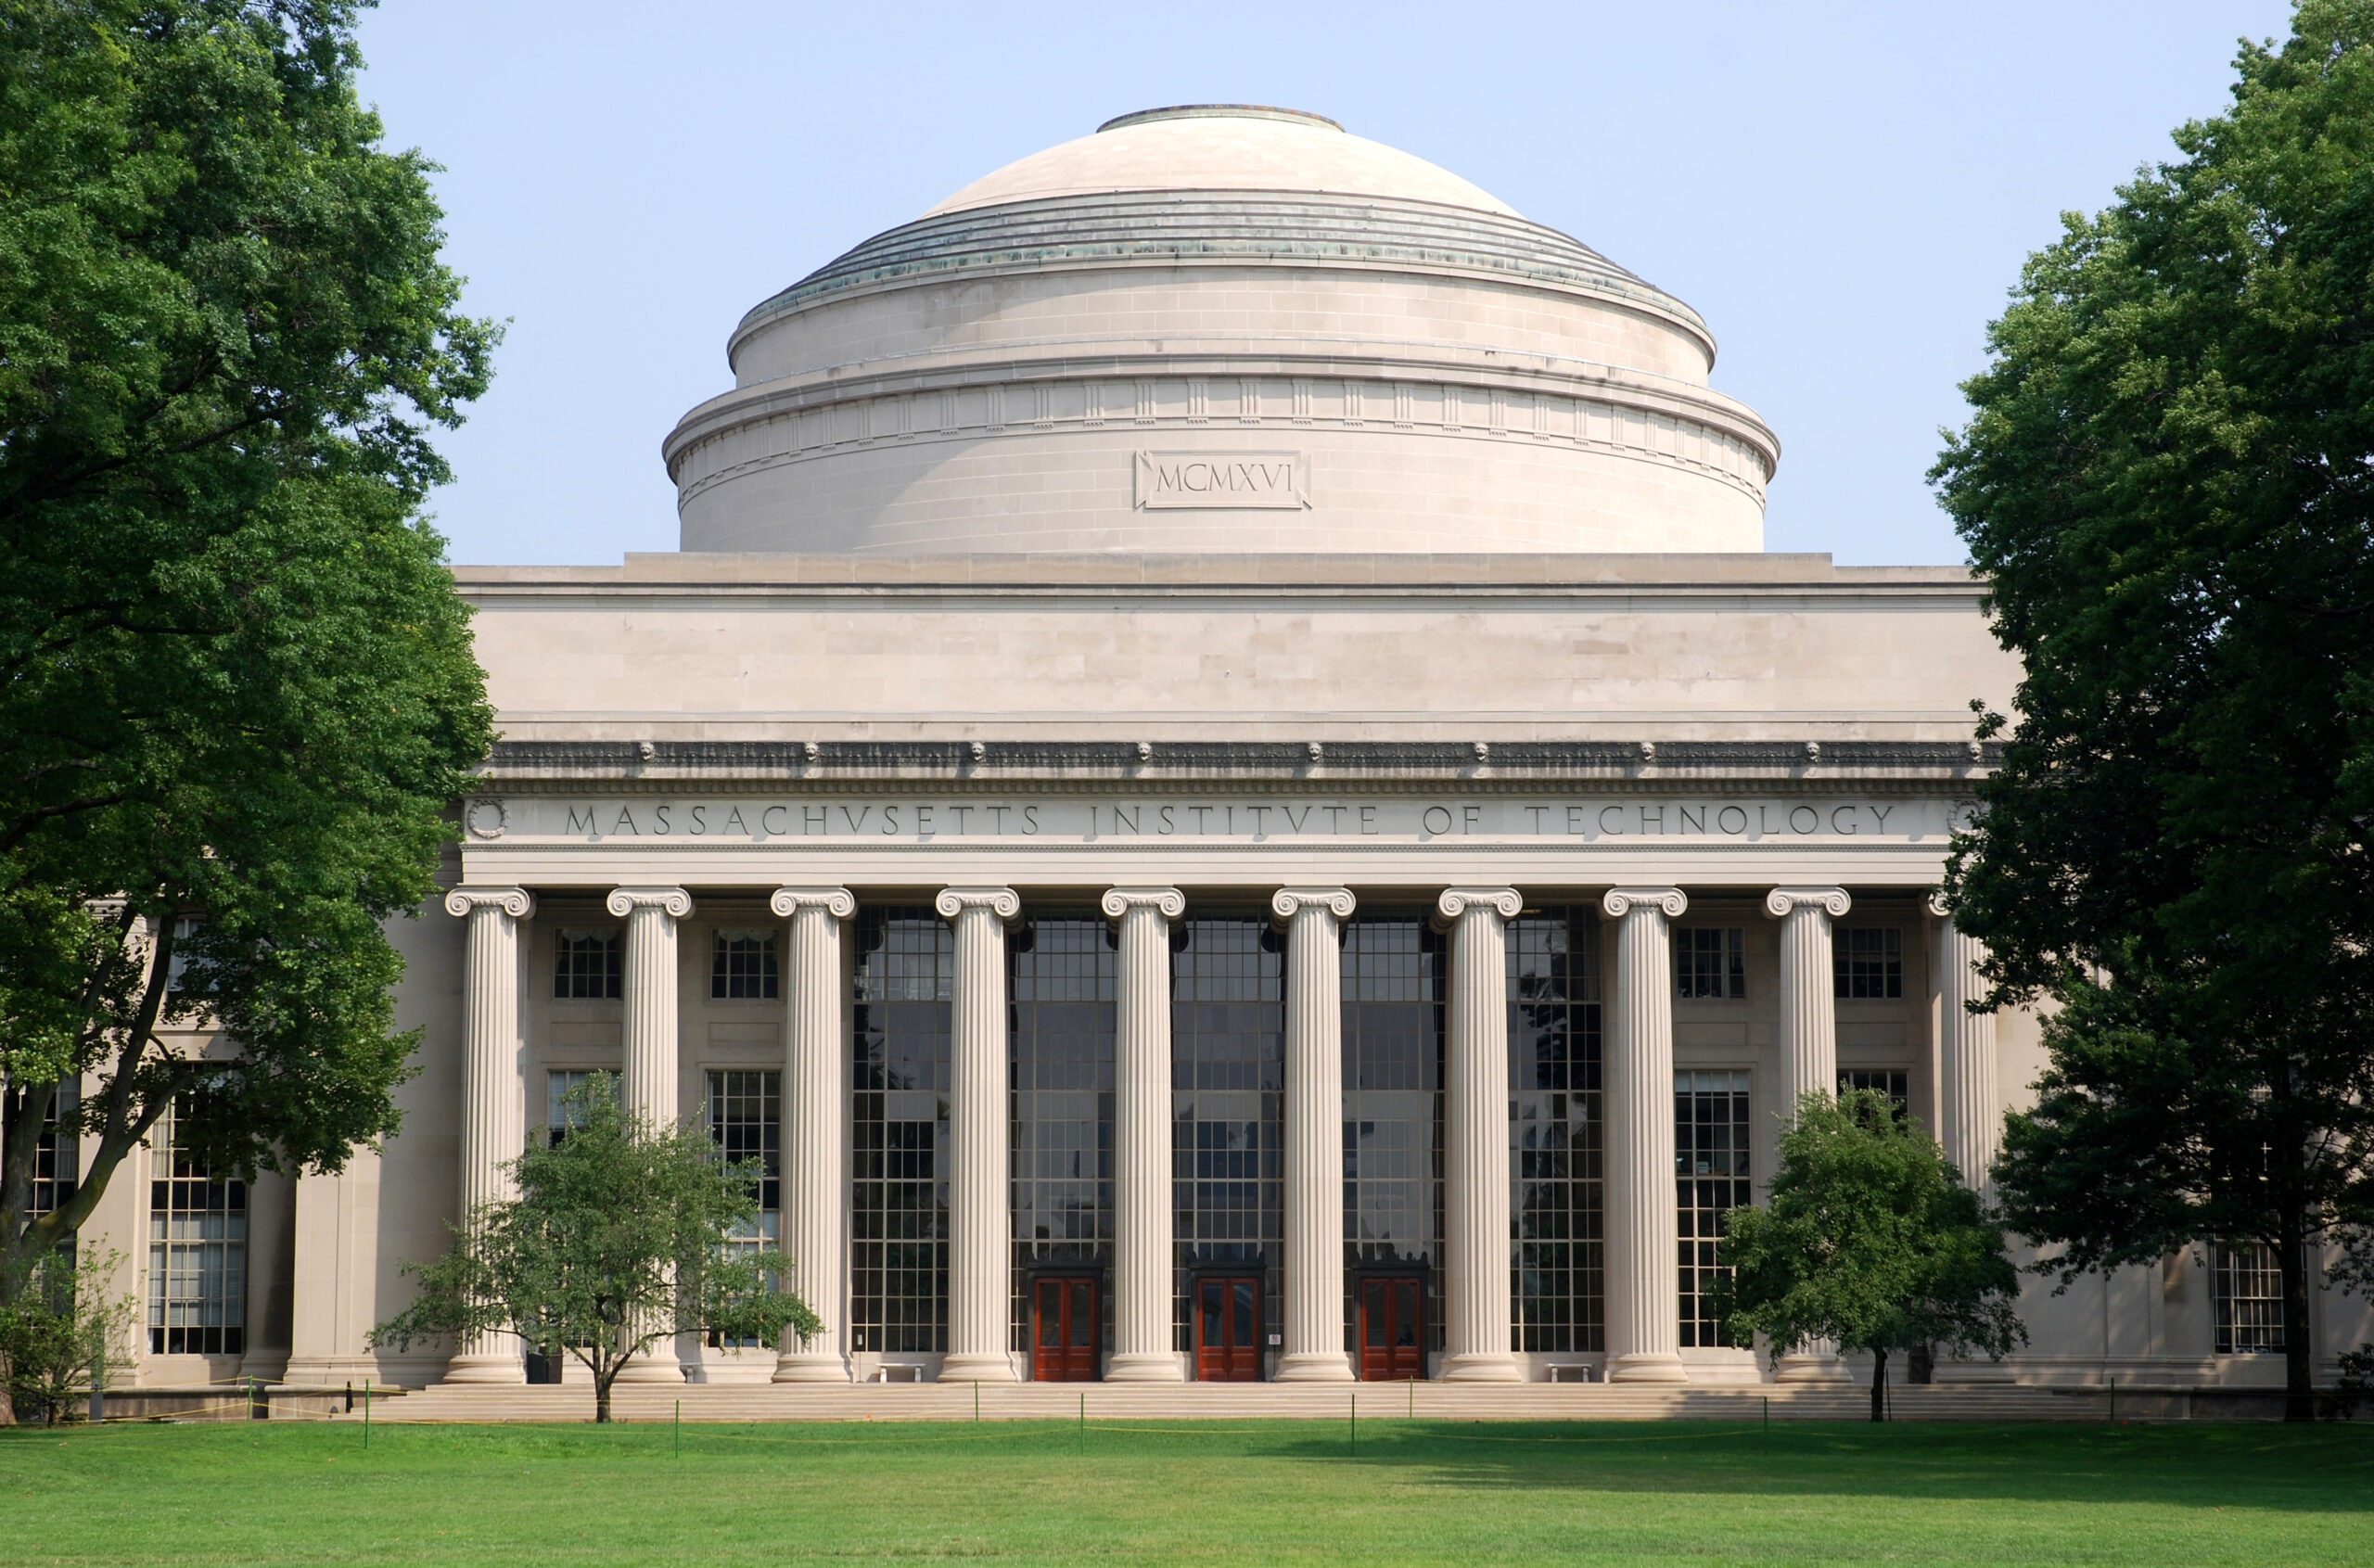
MIT has named Jeremy Rosenberg Chief Information Security Officer, effective November 2026, pulling him from Yale University, where he served as Assistant Vice President for IT and CISO. It is not his first time building a security program from the ground up. Before Yale, Rosenberg was CISO at the University of California, Berkeley, and held technology leadership roles at Simon Fraser University in Canada. That trajectory, three large research institutions in a row, makes him one of a small pool of executives who have repeatedly rebuilt security architecture for organizations with the specific risk profile research universities carry.
At Yale, Rosenberg led a 120-person team responsible for cybersecurity, network services, enterprise storage, and cloud operations, a scope that looks a lot like a mid-size enterprise's combined security and infrastructure organization. His signature project there was a $5 million endpoint detection and response rollout covering more than 25,000 devices, a meaningful commitment for an institution that does not generate revenue the way a commercial enterprise does. At MIT, he will lead institute-wide cybersecurity strategy, strengthen security architecture, and oversee the policies protecting systems, data, and intellectual assets across both research and academic operations.
Why research universities are a proving ground for enterprise CISOs
Enterprise CISOs tend to overlook higher education as a talent source, but the risk profile overlaps more than it first appears. Research universities are structurally decentralized, with dozens of semi-autonomous departments, labs, and research centers that each run their own systems and vendor relationships, not unlike a holding company or a private-equity portfolio of operating units. Security leaders who succeed in that environment have already solved the governance problem that trips up a lot of enterprise CISOs: how to set and enforce a baseline security posture across business units that each believe their work is too specialized for standard controls.
The intellectual property angle matters just as much. Research universities sit on unpublished findings, pre-patent inventions, and federally funded research data that nation-state actors and competitors actively target, often without the institution itself realizing what it holds until something goes missing. That is a sharper version of the IP-protection problem facing any enterprise with an active R&D pipeline, which is exactly why a CISO who has spent a career defending that kind of asset, across three institutions now, brings pattern recognition that is hard to find inside a typical corporate security career path.
The budget number worth benchmarking
Rosenberg's Yale program gives enterprise security leaders a rare, concrete data point: roughly $5 million to cover endpoint detection and response across more than 25,000 devices, or in the neighborhood of $200 per endpoint for the rollout. Vendor pricing for EDR varies widely by contract size, feature tier, and negotiating leverage, so this single figure is not a universal benchmark. It is still a useful anchor for any CISO building a board presentation to justify a comparable rollout, particularly at organizations with a similarly dispersed device fleet and limited centralized IT control over how those devices get used.
What the number does not capture is implementation cost: staff time, change management across a federated user base that resists centralized control, and the ongoing tuning that keeps an EDR platform from drowning a security team in false positives. Any CISO citing this figure to a CFO should frame it as a starting point for the software line item, not the full cost of the program, and should expect the services and staffing cost sitting on top of it to run considerably higher in a commercial setting with fewer volunteer power users than a university campus provides.
What the hire signals about the CISO talent market
A CISO moving from Yale to MIT, both elite research universities with comparable risk profiles and budgets, says something about where top security talent currently has leverage. Rosenberg is not jumping to a Fortune 500 company for a pay bump, the move most security recruiters assume a talented CISO is working toward. He is moving laterally within a sector that evidently values and competes for proven research-institution security leadership on its own terms, which suggests the pool of executives who can run security across a decentralized academic enterprise is smaller than the demand for them.
For enterprise CISOs competing for the same caliber of leadership, that is a signal worth taking seriously. If research universities are willing to bid against each other for this specific skill set, enterprises hoping to poach from that pool should expect to pay a premium and should not assume academic-sector compensation norms will make the hire cheap. It also means the reverse flow, enterprise CISOs moving into higher education, may be rarer than assumed, since the skill set required to run security across a federated research institution is its own specialization rather than a downgrade from corporate work.
The governance lesson for federated enterprises
Strip away the university setting and Rosenberg's mandate reads like a playbook for any large enterprise built from acquisitions, joint ventures, or loosely coupled business units: set institute-wide strategy, strengthen architecture, and protect intellectual assets across operations that do not naturally want to be governed the same way. That is the exact challenge facing CISOs at private-equity-backed platforms stitching together multiple acquired companies, each with its own legacy systems and risk tolerance, and the exact challenge Rosenberg has now solved at three separate institutions.
The practical takeaway for enterprise security and technology leaders is to widen the aperture on where comparable experience lives. A candidate's resume listing three universities instead of three Fortune 500 names should not read as a red flag in a CISO search; for organizations wrestling with decentralized governance and high-value IP protection, it may be closer to exactly the right background. MIT's bet is that managing security across a federated research enterprise is a transferable, scarce skill, not a niche one, and the hiring pattern among its peer institutions suggests they agree.