A national-security résumé lands in enterprise security
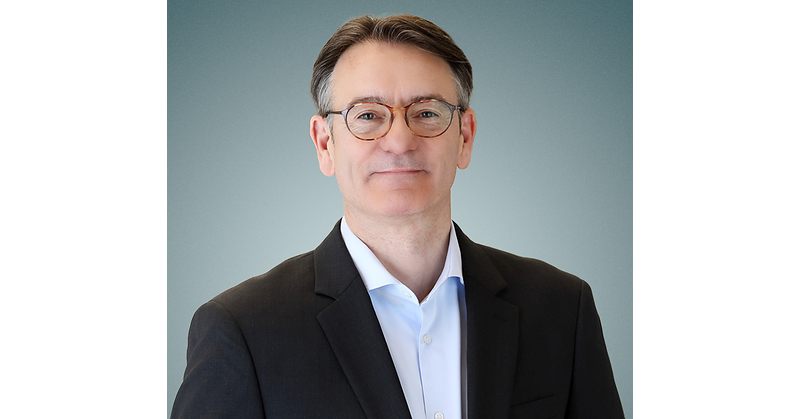
Gigamon, the deep observability company that monitors hybrid cloud networks for more than 4,000 organizations and 83 Fortune 100 companies, announced on September 2 that Grant Yacomeni is joining as chief information security officer. Yacomeni is a U.S. Marine Corps veteran who spent over a decade in cybersecurity and national security roles, including leadership positions inside the U.S. Intelligence Community and Department of Defense, where he directed enterprise security initiatives and managed continuous defensive cyber operations. He also served in cybersecurity roles with the Maryland Army National Guard before moving into the private sector.
This is a departure from the standard CISO hiring path, where candidates typically move between corporate security leadership roles at increasingly large companies. Gigamon COO Gareth Maclachlan's framing of the appointment, emphasizing that Yacomeni has spent his career operating in some of the world's most demanding cybersecurity environments, amounts to a direct pitch that intelligence-community operational tempo predicts enterprise security competence at least as well as a traditional corporate CISO resume. Whether that thesis holds up over time is worth watching, but a company of Gigamon's scale betting on it publicly is itself notable.
Why AI is the explicit hook, not an afterthought
Yacomeni's own quote on taking the job gets specific fast: AI raises the stakes for security leaders because it can act on information at a speed and scale organizations have not faced before. That is a sharper articulation than most vendor press releases manage, and it reflects the actual operational problem enterprise CISOs are wrestling with right now, which centers less on AI models producing bad outputs and more on AI-driven systems and AI-assisted attackers operating at a tempo manual security operations cannot match.
Gigamon's own product, deep observability into hybrid cloud network traffic, is positioned directly against this problem, since defending against speed and scale requires seeing it first. Hiring a CISO whose background is specifically in high-tempo defensive cyber operations, rather than governance, risk, and compliance, signals that Gigamon wants its internal security practice to demonstrate the same operational speed it sells to customers. For a security vendor, a CISO who can speak from lived operational experience about AI-accelerated threats is a credibility asset a compliance-oriented hire would struggle to match.
The observability angle behind the hire
Gigamon's core business is giving security and network operations teams visibility into traffic that other tools miss, particularly in hybrid and multi-cloud environments where blind spots multiply fast. A CISO with a background running defensive cyber operations for national security agencies has direct experience with exactly the kind of large-scale, high-stakes network monitoring that Gigamon's customers are trying to replicate inside their own enterprises, just at a different scale and under a different legal framework.
That operational alignment matters for how customers will read this hire. A CISO who has personally run detection and response at a national-security tempo can speak to product roadmap decisions and customer conversations with a level of specificity that a career compliance executive cannot, and Gigamon is clearly positioning Yacomeni to do exactly that, both internally and in front of the customer base the company is trying to keep ahead of AI-accelerated threats. For enterprise buyers evaluating observability and detection vendors, a CISO with this profile is also a useful reference point when negotiating what the vendor's own security operations actually look like day to day.
What PE-backed security vendors are signaling about talent
Gigamon operates under Elliott Management's Evergreen Coast Capital and the Qatar Investment Authority, which took the company private in a 1.6 billion dollar deal. PE-backed technology companies tend to be more deliberate about executive hires than public companies chasing quarterly optics, because the ownership structure rewards operational improvement that shows up in enterprise value rather than headline management changes. A CISO hire built around demonstrable operational credibility rather than brand-name pedigree fits that ownership incentive closely.
For CISOs and CIOs building out their own security leadership benches, the pattern worth tracking is where military and intelligence-community veterans are landing: increasingly at vendors whose products depend on speed-of-detection claims, where the hire itself becomes part of the product story. That is a specific, narrow signal rather than a general statement about military hiring, and it is worth watching whether other PE-backed security vendors follow the same playbook over the next several quarters as they look for ways to differentiate on operational credibility rather than feature lists alone.
Where to widen your own CISO search
If you are recruiting security leadership for an AI-heavy environment, it is worth widening your candidate search beyond the usual corporate CISO circuit to include people who have operated under sustained, high-tempo threat conditions professionally, since that operational fluency is exactly what AI-accelerated attacks are starting to demand. Military and intelligence-community veterans bring a demonstrated ability to make fast decisions under incomplete information and sustained pressure, a skill set that translates directly to defending against AI-driven attack tooling that does not wait for a quarterly security review cycle.
The trade-off is that candidates from this background may need more onboarding time to translate government and defense operating norms into corporate governance, budget, and vendor management processes. That onboarding cost is real, but Gigamon's bet, backed by its private equity owners, is that the operational credibility gained is worth the ramp time required. Any enterprise considering a similar hire should plan for that transition explicitly rather than assuming the operational skills transfer without friction.