A manifest file was enough to monetize 13.4 million users
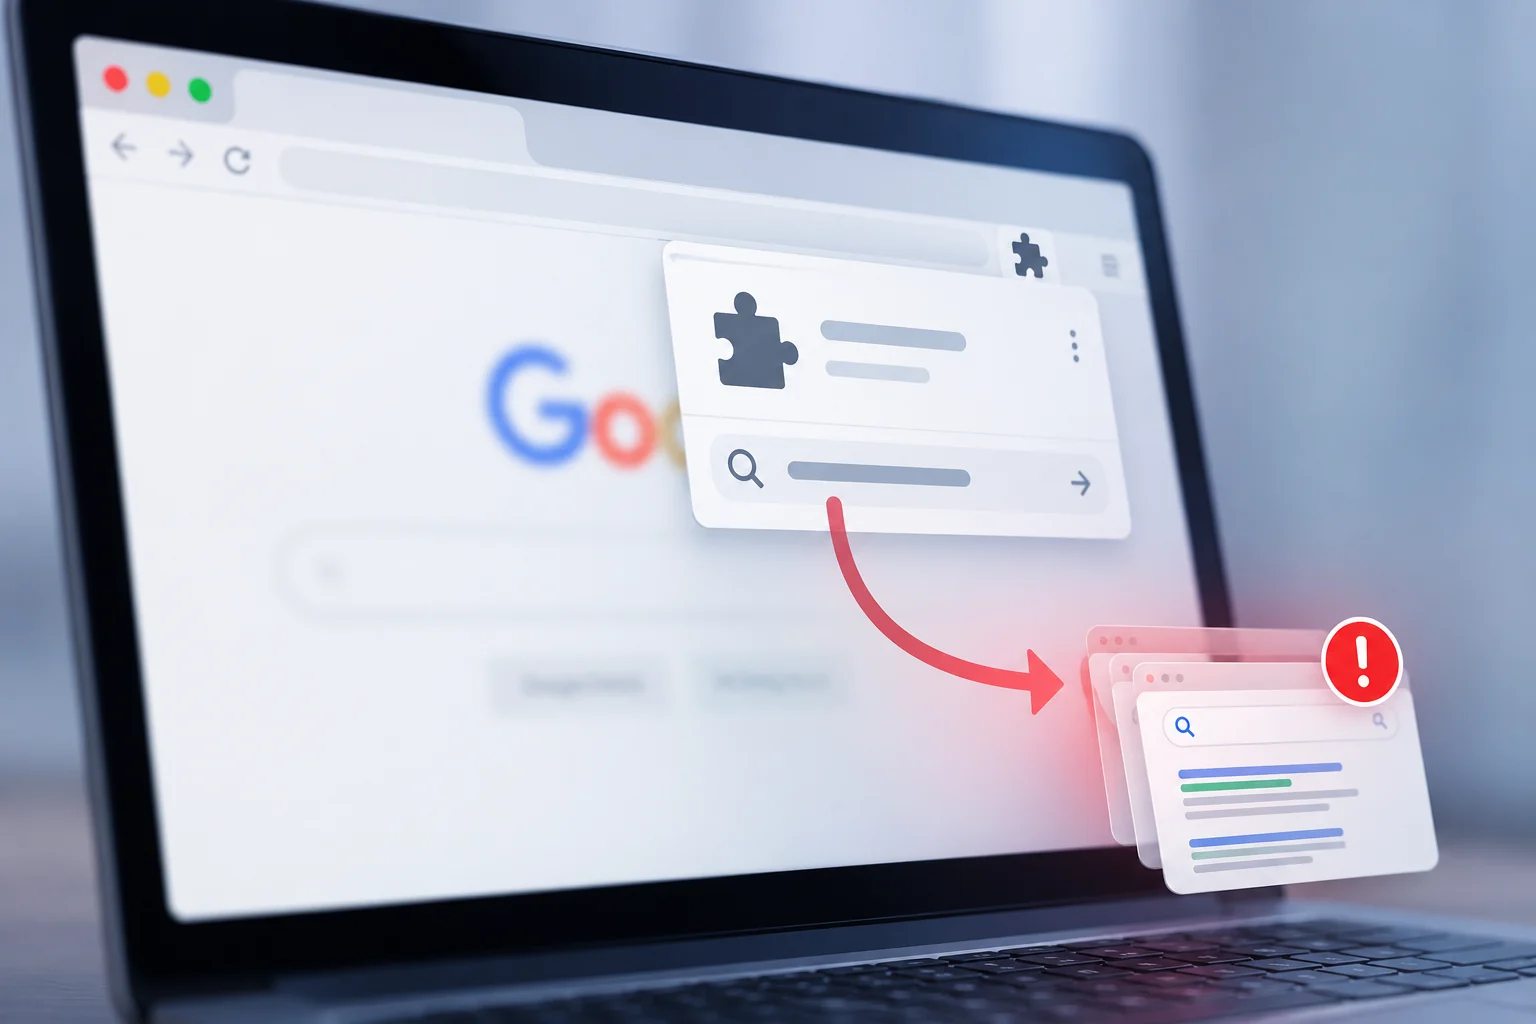
Researchers at Socket found 319 Chrome extensions, collectively linked to 13.4 million reported installations, quietly rerouting users' default search queries through a server the extension operators controlled. The mechanism exploited a legitimate Chrome feature, chrome_settings_overrides, which lets a developer change certain browser settings including the default search provider, a capability meant for search engines and productivity tools to offer users a convenient default rather than for anyone to covertly intercept every query a person types.
What makes this campaign worth a second look is how little code it actually required. Several of the extensions amounted to a manifest file and a handful of icons, with no extensive background scripts and none of the sensitive permission requests that typically draw scrutiny from a security review or a cautious user reading an install prompt. That minimalism is precisely what let them sit unnoticed for as long as they did.
The search results still worked, which is the whole trick
Users who installed one of these extensions kept getting search results. That is the detail that makes this different from a typical malicious extension, where something breaks or something obviously unwanted happens and a frustrated user eventually goes looking for the cause. Here, the redirect happened silently in the background, the operator's server logged the query, and the user received results that looked and functioned like an ordinary search, with no visible disruption to point them toward uninstalling anything or even suspecting that anything unusual was happening to their browser at all.
Socket says the operators monetized this setup primarily through advertising referral revenue generated by the redirected traffic, treating millions of ordinary searches as a continuous, invisible revenue stream rather than a one-time payload delivery. That business model only works if users never notice, which is exactly why a redirect this quiet can run at a scale most malware campaigns never reach, and exactly why it took 13.4 million installs accumulating before anyone outside the operators' own network noticed the pattern at all.
An invisible distribution channel on a trusted store
All 319 extensions were hosted on the official Chrome Web Store, the platform most enterprises implicitly trust as a baseline filter against obviously malicious software. Most of the listings were unlisted, meaning they never appeared in the store's own search results or Google's general web search, so a user or an IT admin trying to verify an extension's legitimacy by searching for it directly would find essentially nothing to confirm or deny its presence on the platform at all.
Distribution instead ran through paid advertising, including campaigns placed on Google Ads and other ad networks, which pointed users directly to the unlisted install page rather than relying on organic store discovery to find an audience. Socket's researchers note that exactly how these extensions got past Google's own Chrome Web Store review process remains unclear, which is itself a notable gap in a review pipeline most organizations treat as a sufficient control on its own without any further internal verification layered on top of it.
Why an intermediary server turns a nuisance into a real risk
The redirect-for-ad-revenue model Socket documented sits closer to a potentially unwanted program than conventional malware, and that classification matters for how seriously a security team might initially treat it. But the architecture carries a risk beyond nuisance advertising: because the redirect routes through a server the operator controls rather than resolving directly, that operator can change where searches land at any moment, without updating the extension code or triggering a new Chrome Web Store review.
That flexibility means an extension installed today as a relatively harmless ad-revenue redirect could, at the operator's discretion, start sending users to credential-harvesting pages or malware distribution sites tomorrow, with zero code change on Google's side to catch. Any enterprise that allowed one of these 319 extensions onto employee machines has a standing exposure that updates itself outside the normal software update and review cycle entirely, and that server-side switch stays invisible to every control that depends on inspecting the extension's published code rather than monitoring the traffic it actually generates in production.
The governance gap this exposes on managed endpoints
Most enterprises apply rigorous software approval processes to anything that touches a corporate device directly, while leaving browser extensions almost entirely to individual employee discretion. That gap exists because extensions feel lightweight and low-stakes compared to installed applications, yet an extension with chrome_settings_overrides permissions sits in the exact same trust position as a network proxy, quietly intermediating every search request an employee makes from a managed device throughout an entire workday without anyone in IT ever seeing the traffic pattern change.
A 13.4 million install footprint before anyone caught this campaign shows how long that gap can persist unaddressed across even well-resourced organizations. Enterprise device management tools already support extension allowlisting and blocklisting at the browser policy level, which means the control to close this gap already exists in most organizations' endpoint management stack today. What is missing is the operational decision to actually enforce it rather than leaving extension installation as unrestricted self-service for every employee on a managed fleet.
What belongs on next quarter's endpoint security checklist
For a CTO or CISO reviewing endpoint controls, this campaign argues for treating browser extensions as a managed software category with the same rigor applied to any other application touching corporate data, rather than as a convenience employees configure on their own. That means extension allowlisting through browser policy, a periodic audit of what is actually installed across the fleet, and specific scrutiny for any extension requesting settings-override permissions regardless of how little code it appears to contain.
The 13.4 million install figure is also a reminder that scale alone does not guarantee scrutiny. A campaign can run across more installs than most targeted enterprise attacks ever reach, precisely because it hid in a category nobody was systematically reviewing in the first place. Closing that blind spot costs little relative to the browser-policy tooling most enterprises already pay for and rarely configure beyond its defaults, and the decision is really about operational follow-through rather than new budget, which makes it one of the cheaper fixes on any CISO's current list.