A new twist on an old problem
Browser-native AI assistants are being rolled out fast, and the security research is catching up in real time. BragJack, disclosed on September 19 by researcher Gal Weizman of Forever Security, targets the seam between the AI model doing the reasoning and the browser component that actually has privileged access to network requests, tabs, and page content. Weizman describes the technique as "Prompt Forcing," and draws a specific distinction from conventional prompt injection: instead of hiding malicious instructions inside content the AI might read and be tricked into following, a malicious extension delivers a complete, fully-formed prompt directly to the agent, which then carries it out using the browser's own legitimate privileges.
The mechanism relies on Chromium's declarativeNetRequest API, a legitimate extension capability meant for things like ad blocking and request filtering. BragJack repurposes it to intercept and manipulate network requests, weakening security headers and redirecting resources in ways that let an attacker steer what the AI assistant sees and does. Because the attack rides on a standard, sanctioned extension API rather than exploiting a memory corruption bug, it is a design-level weakness in how these assistants are integrated into the browser, not a simple coding error that a single patch definitively closes.
Five products, one shared architecture problem
The research covered Google Chrome's Gemini Live, Perplexity Comet, Microsoft Edge, Opera Neon, and Anthropic's Claude in Chrome, meaning nearly every major browser-native AI assistant currently shipping was affected by some variant of the technique. That breadth is the real headline. This is not a single vendor's implementation bug; it is evidence that the industry converged on a similar architectural pattern, an AI model with reasoning capability paired with a browser extension layer holding real privileges, and that pattern has a shared weak point regardless of who built it.
Two CVEs came out of the disclosure so far, CVE-2026-0628 for Chrome and CVE-2026-55945 for Microsoft Edge, and both companies have already shipped fixes. Bug bounty payouts across the affected vendors totaled more than $20,000, ranging from $600 to $7,000 per finding, a reasonable but not enormous sum given how many products and vendors were involved. There is no evidence of active exploitation; Weizman disclosed the research responsibly before publication, giving vendors time to patch, which is the outcome you want from this kind of work but does not eliminate the underlying design question.
Why enterprises should care before their own AI browser rollout
Enterprises rolling out AI-enabled browsers to employees, or evaluating them for procurement, are effectively adopting a new privileged software layer that sits on top of every web session an employee runs, including banking portals, internal tools, and SaaS admin consoles. BragJack demonstrates that a malicious or compromised extension, something security teams already know how to worry about, can now be a path to hijacking an AI agent's own elevated privileges rather than just the browser's. That expands the blast radius of extension security from "steal cookies and form data" to "impersonate a trusted AI assistant acting on the user's behalf."
Practically, this argues for extension allowlisting policies that specifically account for declarativeNetRequest permissions, not just broad categories like "reads all site data." Security teams evaluating AI-enabled browsers should ask vendors directly how they isolate the AI assistant's execution context from extension-level network manipulation, and whether that isolation was tested against exactly this class of attack. It is also a reminder that a proof-of-concept with no confirmed in-the-wild exploitation today is still worth acting on now, since the gap between disclosed research and weaponized attack has been shrinking across nearly every category of AI security this year.
The responsible disclosure worked, but the clock is now public
It is worth giving credit where it belongs: this is disclosure working as intended. Weizman reported the technique to five vendors, gave them time to patch, and published only after fixes shipped for Chrome and Edge, with no evidence any real attacker used the technique first. That is a meaningfully better outcome than the pattern in several of this week's other disclosures, where exploitation preceded the patch. Bug bounty programs paying out over $20,000 across vendors for this class of research is also a reasonable signal that companies are taking browser AI security seriously enough to fund it, not just react to it after the fact.
The risk now is that publication itself becomes a blueprint. BragJack's mechanics, using a sanctioned extension API to intercept and manipulate the interaction between an AI assistant and its browser privileges, are public, reproducible, and apply conceptually to any browser AI assistant Weizman did not test, including ones still in beta or preparing to launch. Vendors not named in this research should not read that as clearance; they should read it as a checklist of what to test before shipping their own AI assistant integration, and enterprises evaluating unreleased or newly launched products should ask directly whether the vendor has tested against this exact technique.
The roadmap implication
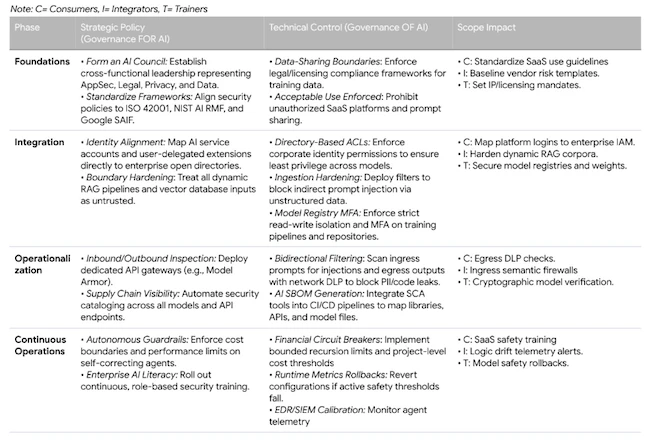
For CIOs weighing AI browser adoption, BragJack is a reason to slow the default-on rollout of browser AI assistants to the general employee population until vendors can answer specific architecture questions about privilege separation, short of halting pilots outright. Treat the browser AI assistant layer the way you would treat a new privileged agent identity: scoped permissions, monitored network behavior, and a documented incident response path if an extension is later found to be malicious. That is a governance cost, not a large capital one, and it belongs in the same review cycle as any other new agent surface entering the environment.
Longer term, this strengthens the case for security teams building AI governance frameworks that explicitly include browser extensions and AI browser assistants as a tracked asset category, alongside SaaS applications and API integrations, rather than leaving them to fall under generic "browser security" policy that predates agentic AI. The vendors here responded quickly and the bounty program worked as intended, which is a reasonable model for the rest of the industry to point to, but the underlying lesson is that every new AI integration point deserves the same adversarial scrutiny before broad deployment, not after.